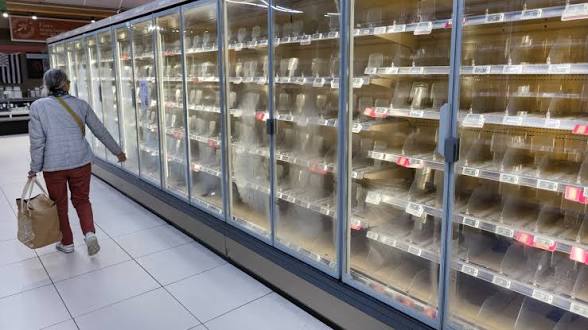

A cyberattack targeting refrigeration systems disrupted hundreds of supermarkets across France overnight on October 11–12, 2026, forcing retailers to discard large quantities of fresh and frozen food.
The attack reportedly affected between 250 and 350 stores initially, with subsequent reports indicating that more than 500 outlets may have been affected. Major retailers hit included Intermarché, Netto, Coopérative U, Carrefour, Monoprix and E.Leclerc.
The hackers reportedly gained remote access to internet-connected refrigeration management systems and manipulated their settings, triggering prolonged defrost cycles that pushed temperatures in some units to 50°C (122°F).
According to reports, the attackers extended defrost cycles from approximately one hour to eight hours, delaying alarms and allowing temperatures to rise for extended periods before staff discovered the problem.
Intermarché and its sister brand Netto reportedly suffered significant disruption, with hundreds of stores affected. Coopérative U reported attacks on more than 100 outlets, while approximately 80 Carrefour stores and some Monoprix locations were also reportedly impacted.
The incident resulted in substantial food waste as retailers removed products that could no longer be guaranteed safe for consumption. Some stores also reported equipment damage and localised fires after refrigeration units overheated.
Although the full financial impact remains uncertain, early estimates suggest losses could reach millions of euros, with individual retailers facing considerable costs from discarded stock and damaged equipment.
Outdated Refrigeration Systems Under Scrutiny
Investigators have linked the attack to vulnerabilities in refrigeration control systems manufactured by Danish company Danfoss. Reports indicate that attackers targeted older equipment running outdated firmware, potentially allowing them to manipulate refrigeration settings remotely.
Cybersecurity researchers had previously identified vulnerabilities affecting certain Danfoss control systems and warned about the risks posed by internet-exposed equipment.
The incident has raised concerns about the security of connected industrial devices, particularly systems responsible for essential services such as food preservation and distribution.
French Authorities Launch Investigation
The Paris prosecutor’s office has opened an investigation into the attack, while Prime Minister Sébastien Lecornu has tasked France’s National Cybersecurity Agency, ANSSI, with examining the incident and coordinating with relevant partners.
Similar refrigeration-related disruptions have also been reported in other European countries, although the extent to which those incidents are connected remains unclear.
No individual or group had publicly claimed responsibility at the time of the initial reports.
The attack has renewed calls for stronger cybersecurity measures, regular software updates and tighter controls on remote access to industrial equipment, highlighting how vulnerabilities in seemingly ordinary supermarket infrastructure can cause widespread economic and operational disruption.
By Musekir Faisat Omolara